Your AI skills can read your files. Almost nobody checks them first.
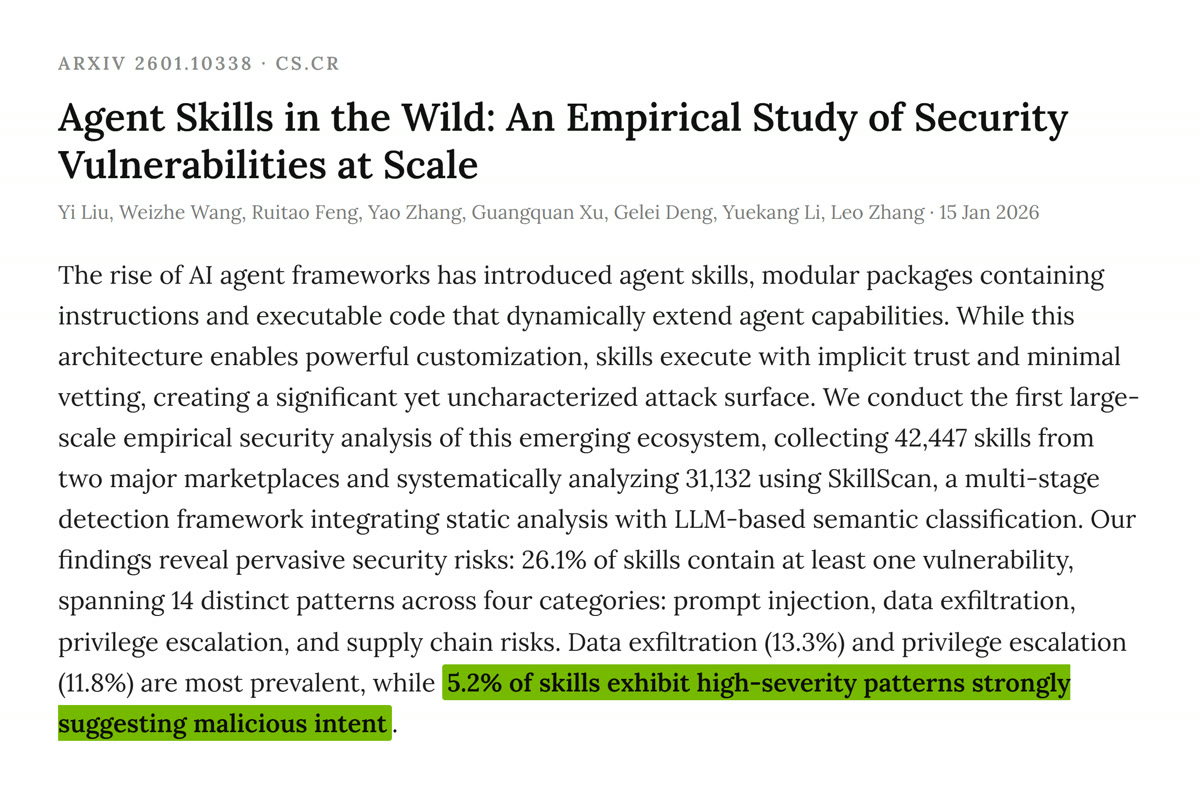
A study of 31,132 agent skills found that 26% carry a security vulnerability and 5.2% look outright malicious. NVIDIA built a free scanner that checks any skill before it ever touches your machine. Here is the whole thing in one page.
uv tool install git+https://github.com/NVIDIA/skillspector.git
01 · THE PROBLEMThe numbers that started this
Researchers collected 42,447 agent skills from two major marketplaces and analysed 31,132 of them. The paper is public and the abstract carries both headline numbers.
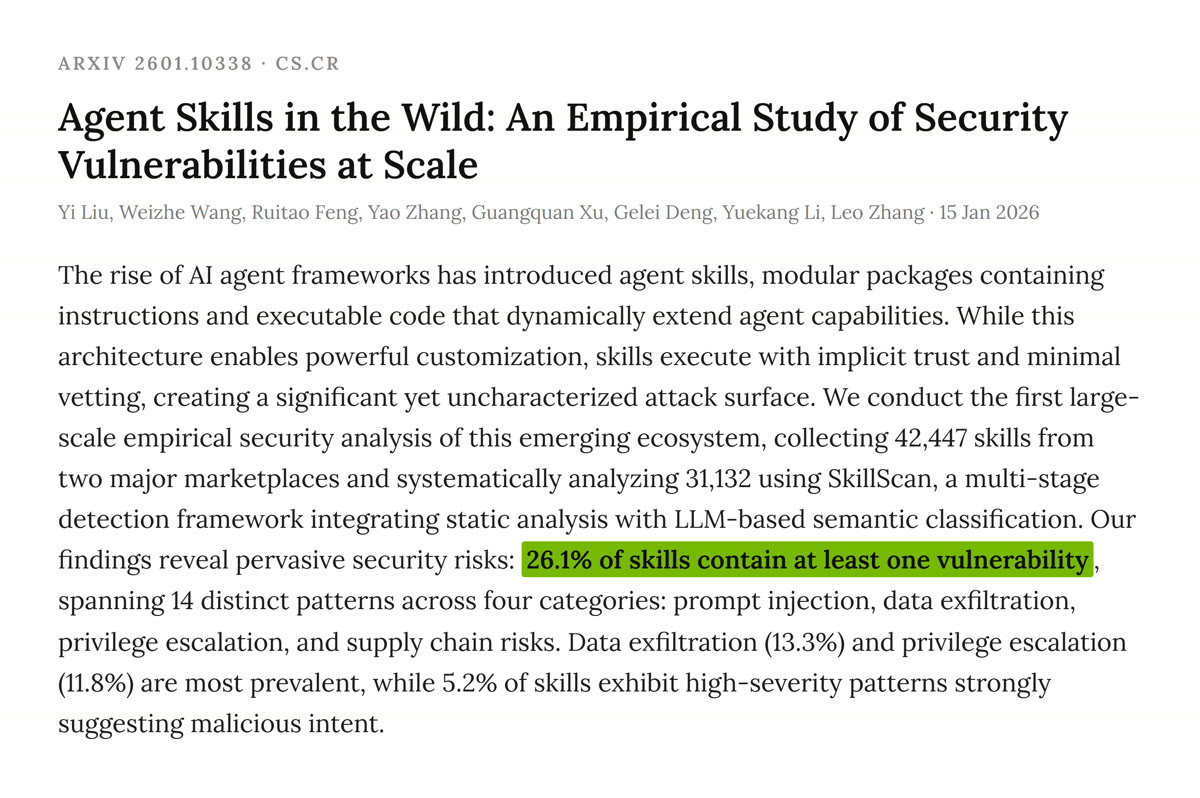
The two most common problems were data exfiltration at 13.3% and privilege escalation at 11.8%. Skills that bundle executable scripts were 2.12x more likely to contain a vulnerability than instruction-only ones.
Why this is worse than a bad npm package. When you install a skill it gets your file system, your network, your environment variables, and sometimes your model's system prompt. There is no permission gate between the install command and the code running.
02 · THE FIXNVIDIA SkillSpector
A free, open source scanner that sits between you and any skill you are about to install. Point it at something, it tells you whether to install it.
Install it
uv tool install git+https://github.com/NVIDIA/skillspector.git
Run it on anything
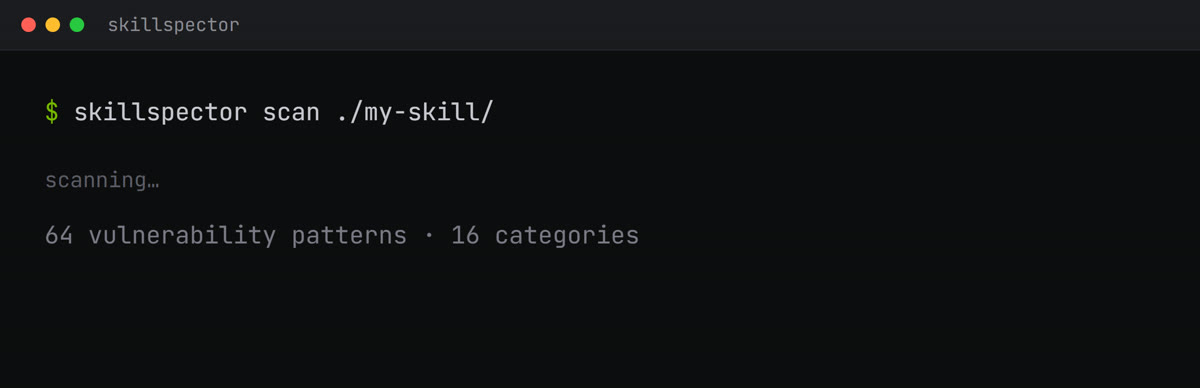
- A folder:
skillspector scan ./my-skill/ - A GitHub repo:
skillspector scan https://github.com/user/my-skill - A zip:
skillspector scan ./my-skill.zip - A single file:
skillspector scan ./SKILL.md - JSON out for CI:
--format json --output report.json - Static only, no LLM:
--no-llm
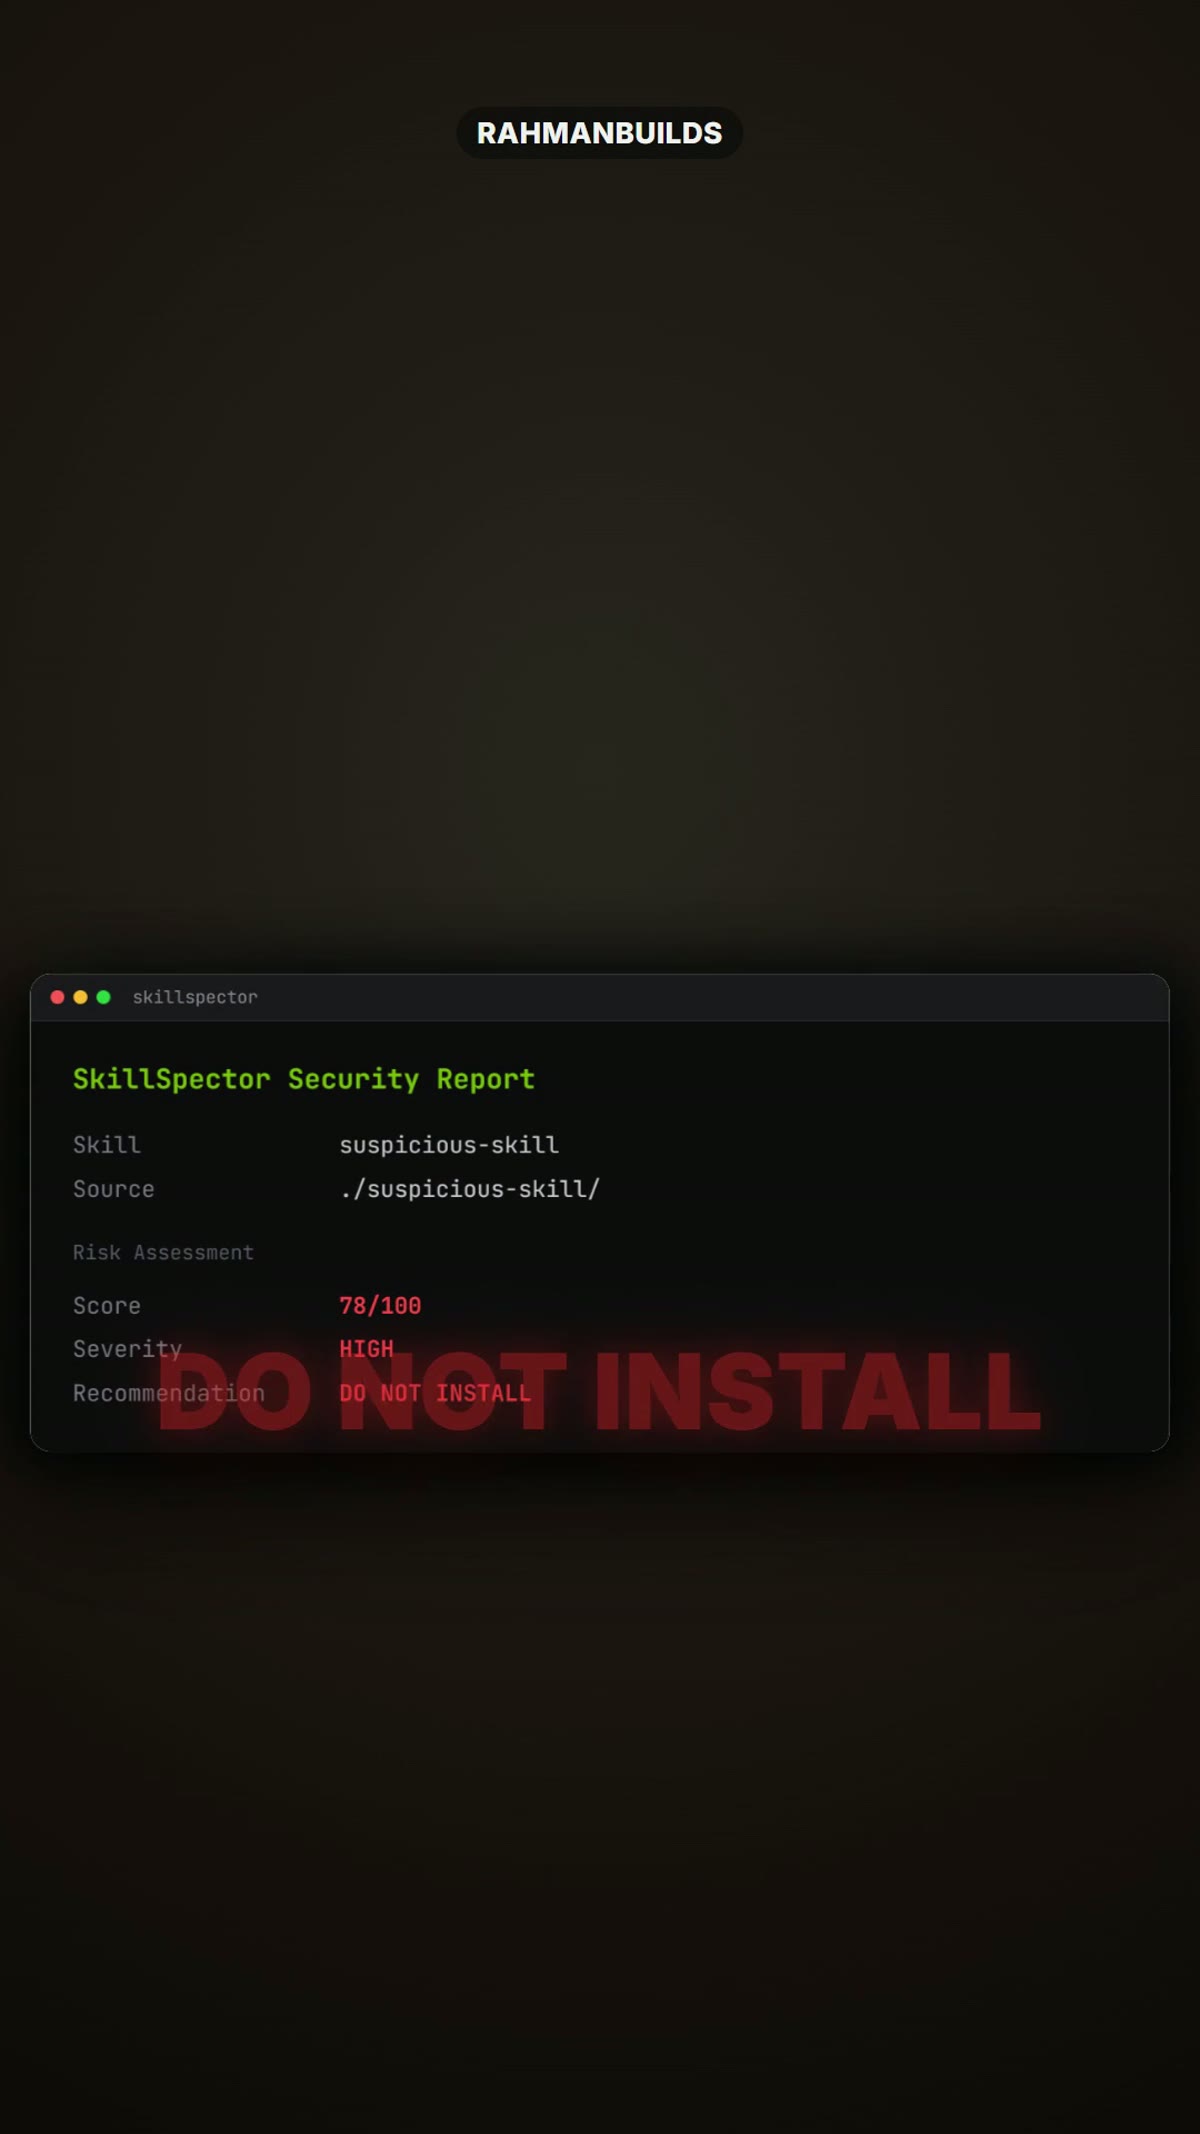
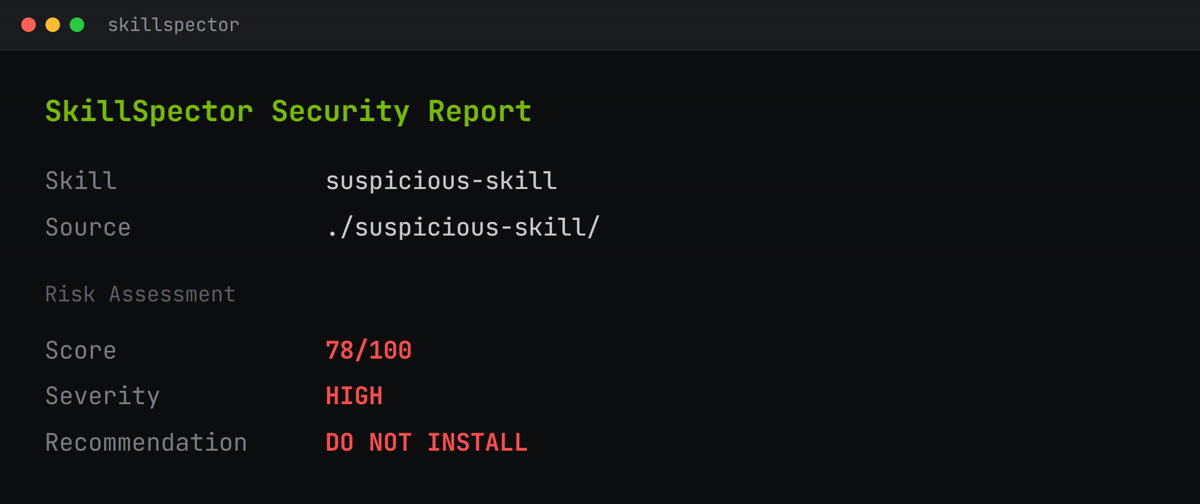
03 · THE ANSWERA score out of 100
Every scan ends in one number and one recommendation. This is the part that makes it usable in seconds rather than minutes.
What it actually looks for
17 categories, 64 patterns. The ones that matter most for a skill you found on a marketplace:
- Prompt injection: instructions hidden in the skill that hijack your agent
- Data exfiltration: code that quietly ships your files or keys somewhere
- Privilege escalation: a skill reaching for more access than its job needs
- Supply chain: a poisoned dependency riding along
- Tool misuse and rogue agent: tools called in ways they were never meant to be
- System prompt leakage: your instructions being read back out
- MCP tool poisoning: the MCP-specific version of the same trick
04 · THE HONEST PARTWhat a scanner cannot do
A clean score is a strong signal, not a guarantee. Security researchers have shown that scanners in this class can be evaded by a determined author, and the LLM layer is optional and imperfect. Treat it as the bouncer at the door, not the whole security team. For anything that will touch real credentials, read the skill yourself too.
The habit worth building: scan before install, every time. It costs seconds and it catches the 1 in 4 that has a real problem.
05 · THE REELWhere this came from